Source Protection/Runs at the customer
Runs on their servers. Readable only while it runs.
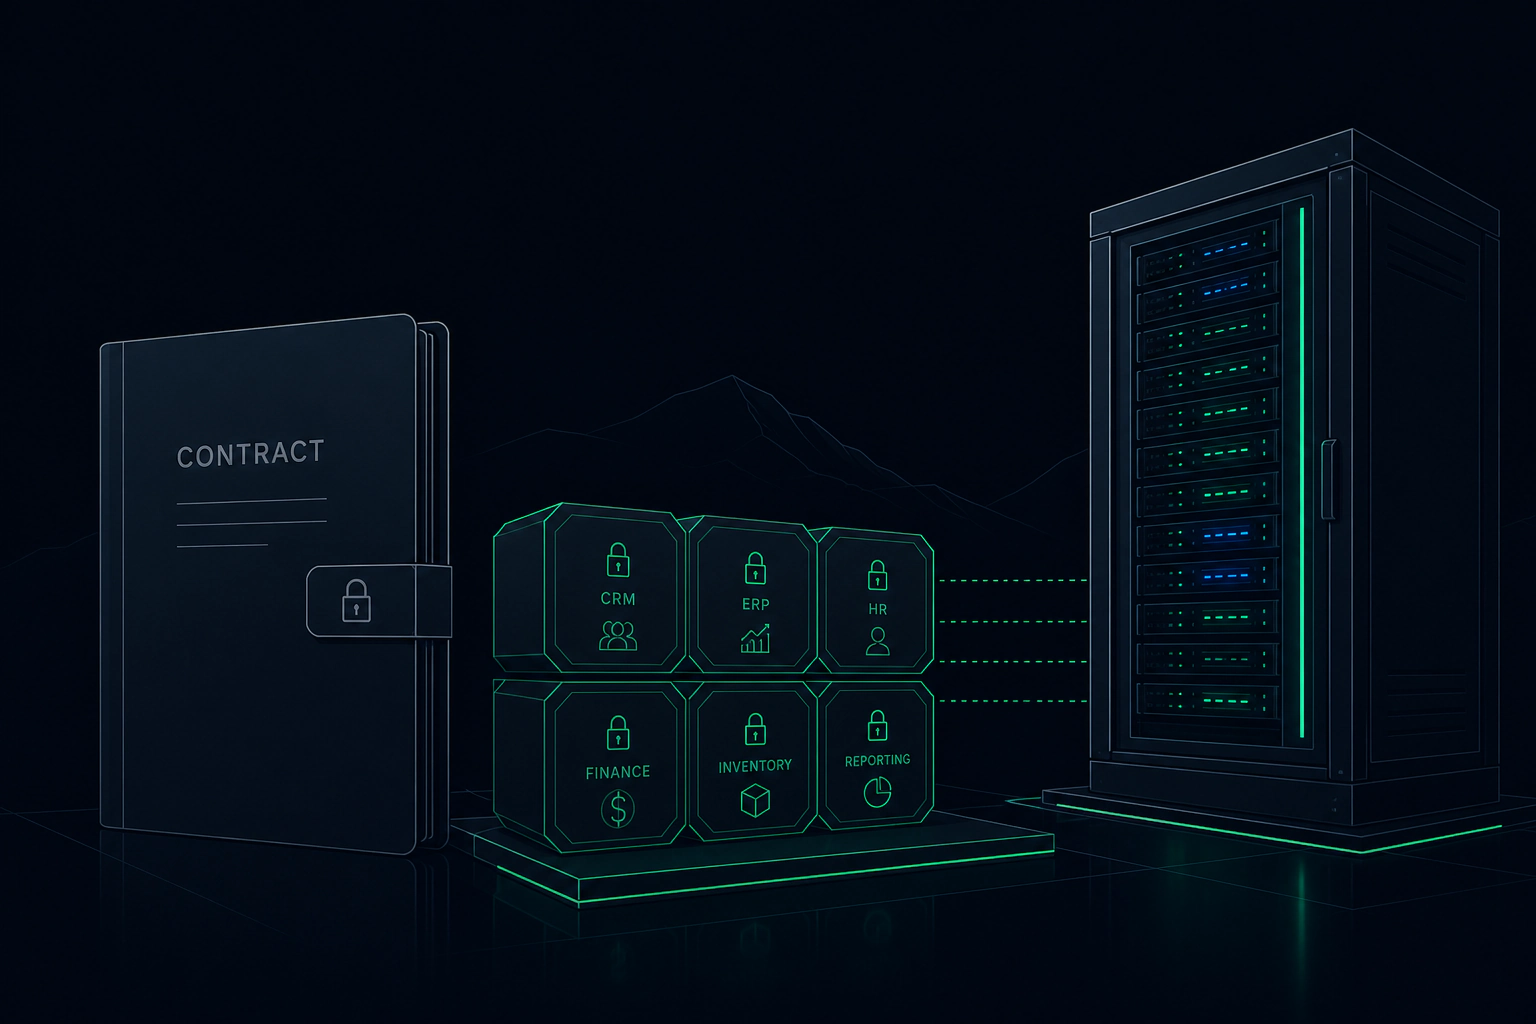
Your customer deploys as normal. The locked parts open for the running software and nowhere else.
Their servers
- Software started
- Key checked with NakodaX
- Locked parts opened in memory
- Nothing written to disk
How it runs at the customer.
A protected release runs on the customer's own servers. When the software starts, a small runtime checks the customer's key and opens the locked parts in memory only. Nothing readable is written to disk, and a copy of the repository is only locked files.
They add a small package
The customer adds the NakodaX runtime to the app and starts it the usual way.
You hand them one page with the steps and the key.
The software checks in
When it starts, it asks NakodaX whether the key is good. If it is, the locked parts open for that running process.
Open in memory only
The code is readable while the software runs, and only there. Nothing readable is left on their disk.
No key, no code
Without a valid key the locked files stay locked. A copied repository is only locked files.
The software checks in when it starts and at regular intervals, so it suits connected customers.
Who uses it.
Software vendors whose customers want it in their own data centre
Say yes to on premises without handing over how it works.
Sellers to banks, insurers and other regulated customers
The software runs inside their walls with your logic locked.
Companies running their software at partners and resellers
A partner runs it, and you hold the key.
Runs at the customer questions
Does the customer need an account with NakodaX?
Which languages work?
Can it run offline?
More Source Protection features
Watch and read
Ship the software. Keep the secret.
Tell us what you deploy and where it needs to run. We will show you how it would work. Already a customer? Sign in to your console.