
By NakodaX Marketing team
NakodaX ·
NakodaX blog/Source Protection·3 min read
Protected by NakodaX.
An encrypted repository looks like any other repository from the outside. Folder names, file names and the README are readable. The source files are encrypted data that show random bytes when you open them. You can clone ours and check this yourself in one minute, with no key and no account.
By NakodaX Marketing team
NakodaX ·
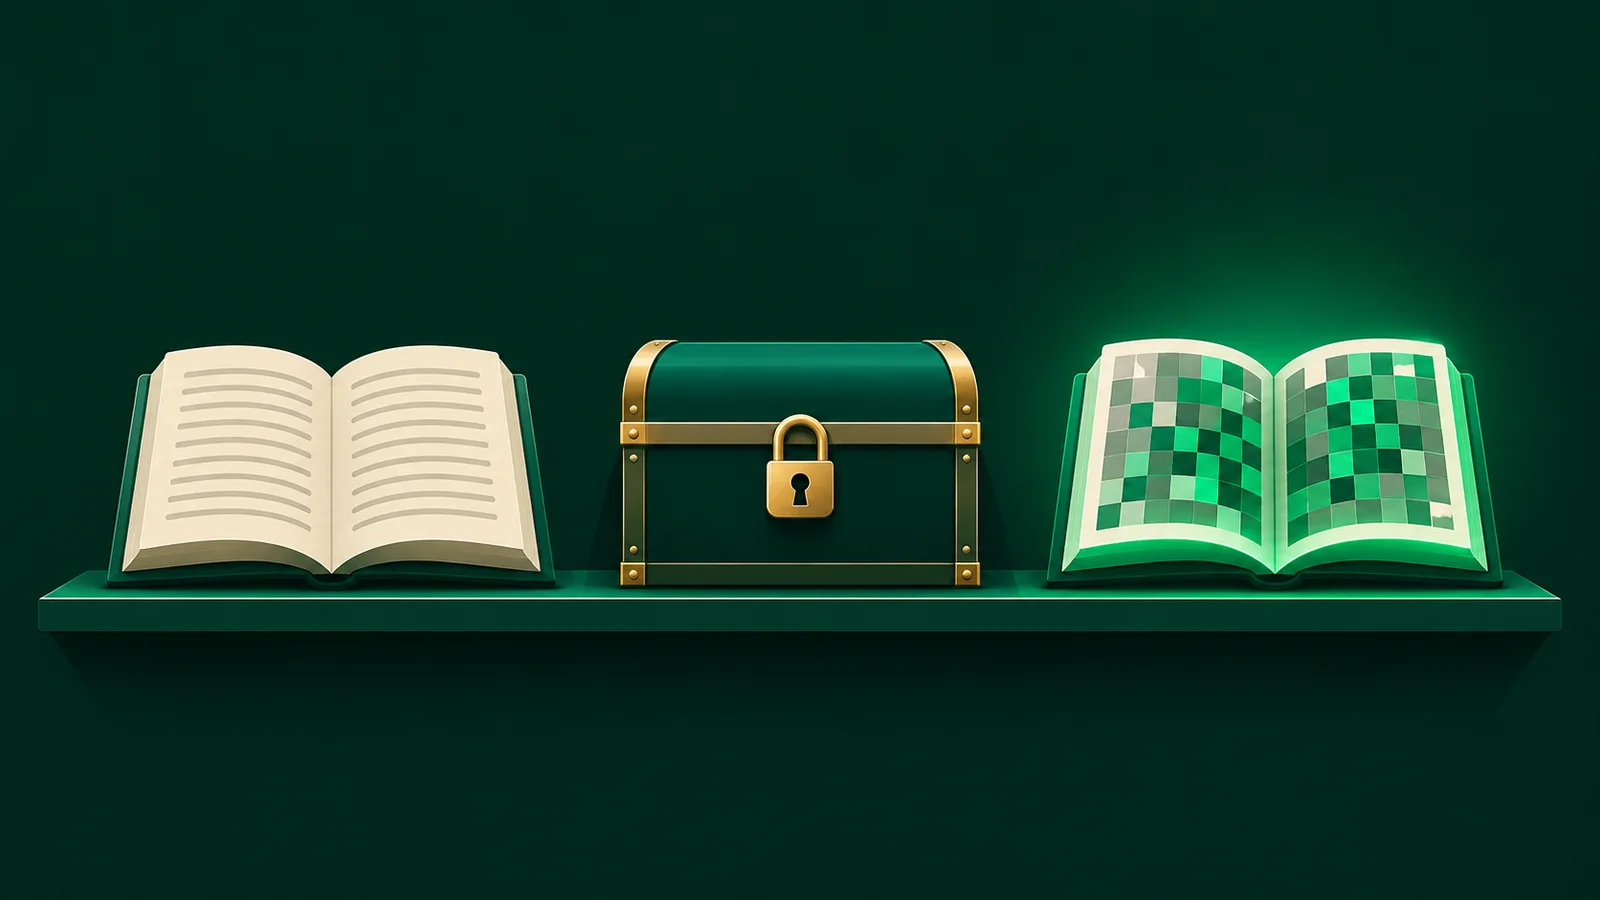
A repository can be public and still unreadable.
For years, GitHub has had two kinds of repository. A public one, which anyone can read. A private one, which only a few people can see.
Today we are introducing a third kind: a repository that is public and still unreadable.
We protected our own source code with NakodaX Source Protection, and then we made it public with confidence. Anyone can clone it. Nobody can read it without a key.
You can open four of them now: nkx-source-protection, nkx-data-protection, nkx-document-protection and nkx-sample-app. This post shows what you see when you open one, and how to check it in about a minute.
The repository page looks normal. There is a README, a license file and a folder for each part of the product. Folder names and file names are readable, as they are in any repository protected with NakodaX.
Open a source file and you do not see code. You see random looking bytes. Each file is encrypted with AES 256 GCM, using its own key. A small manifest file, which is just a list of the files, sits beside them and holds no readable code.
| Part of the repository | Can you read it? |
|---|---|
| README, license and security files | Yes |
| Folder names and file names | Yes |
| Manifest files | Yes. They list the files and hold no readable code |
| Source files | No. They are encrypted |
You do not need an account or a key. You need git and a terminal. These steps use nkx-source-protection.
git clone https://github.com/nakodax/nkx-source-protection.git
cd nkx-source-protection

git ls-files '*.nkxc' | wc -l
head -c 96 backend/src/app.ts.nkxc | xxd
grep -l -a -E '^(import|export|def|class|function) ' -r --include='*.nkxc' . | wc -l
What does this show? Every source file is encrypted. Without a key, all you get is random bytes.
A claim about protection is easy to make and hard to believe. A public repository lets you test it. You can look for yourself instead of taking our word.
It also answers a question buyers often ask: what does Source Protection look like when it is applied? The answer is a repository you can clone today.
If you want to go one step further, unlock the sample app with its free trial key. It is the same idea, with a key that lets you run the code. The full story is in Can you ship your source code to a customer without them reading it?
Choose the files that hold your business logic. Source Protection finds the files worth protecting, encrypts them and publishes a protected copy. You can then share that copy with a customer, a contractor or a partner, or leave it in public. The chosen files stay unreadable.
People who need to build against the code get stand ins. A stand in has the same shape as the real file, with placeholder bodies. This is how a team can work with contractors on sensitive code without handing over the real files.
If your build has to read the protected files, see how to protect source code in a CI build.
You cannot read or run these repositories the way we do. Without a key, the source files stay encrypted. That is the point.
Are you a customer or a prospect, and do you want to review our code from a security point of view? Contact us and fill in the form, or email support@nakodax.com with the subject Source review. Tell us who you are and what you want to check. We agree terms with you first, then arrange a live walkthrough or access for a limited time.
You can clone a repository, open any file and see that it is encrypted. That is what protected code looks like from the outside.
Related product
Let vendors and customers build or run software without receiving selected proprietary source code in readable form.
See how it worksStart a free trial, or tell us what you share and with whom, and we will show you how NakodaX handles it.
Real situations, and the video where there is one, on the same problem.
Video
When software has to run in a customer or vendor environment, see how NakodaX keeps selected proprietary components out of the readable release.
Watch (3:29)Situation
Developers keep copies of the code they work on. When they leave, the copy leaves too. With AI tools, it can become a competitor’s product in weeks.
Read moreSituation
Your model’s edge is in the code around it: how features are built, how it is trained, how results are adjusted. That code is plain Python, and it is easy to take.
Read more
New to NakodaX? Watch the overview
A full walkthrough of how NakodaX helps a business keep control of documents, business data and source code after they are shared, moved or deployed.
Watch the video (8:49)
Source Protection · 2 min read
Removing a leaver's access does not remove the copy on their laptop. Here is a checklist for protecting the key code files before an engineer leaves.
October 2, 2026
Source Protection · 2 min read
Contractors need to build and test, not to hold your key logic. Here is how stand ins and change sessions let them work while the real code stays protected.
October 5, 2026
Source Protection · 2 min read
Most of a codebase is easy to rebuild. A few files are not. Here is how to find them, keep the list short and protect them with NakodaX Source Protection.
September 16, 2026