NakodaX videos/Overview·1:17
Protecting data beyond the security perimeter
AI tools, cloud apps and modern workflows have moved sensitive work past the traditional security perimeter. See how NakodaX follows it there.
Questions this video answers
How can I keep control of data after it leaves my perimeter?
Can an AI tool read a protected document?
Does NakodaX need a copy of my content to do this?
Transcript
NakodaX keeps technical control over your data even after it leaves your perimeter because a contract can't physically stop an external partner from dropping your proprietary files into an AI tool. Let's say you email a highly sensitive document to an external vendor before it leaves your device. NakodaX uses document protection to encrypt the file directly in your browser.
It locks access to specific pages or time frames right then and there. This control scales across workflows. With data pipelines, the system filters out specific warehouse rows.
And if you're deploying software, source protection hides your proprietary logic before it enters a customer's environment. Now, if this system is actively checking permissions and filtering rows in real time, wouldn't NakodaX need a massive readable copy of all your company's data? Not at all.
The architecture completely bypasses central storage. The technical controls travel attached to the encrypted asset, moving directly from the source to the authorized runtime. NakodaX never sees or stores your underlying content.
So that sensitive document from the beginning, it safely reaches the vendor but remains completely unreadable to any AI tool they try to upload it to.
More videos
Data Protection · 1:19
What happens when your data leaves your systems
A contract cannot technically control a copy of your data once it has left your systems. See what NakodaX adds instead.
September 20, 2026
Data Protection · 5:51
How to share business data securely
A partner needs some of your data, not your whole warehouse. See how Data Protection builds a controlled view for each recipient.
September 21, 2026
Data Protection · 1:44
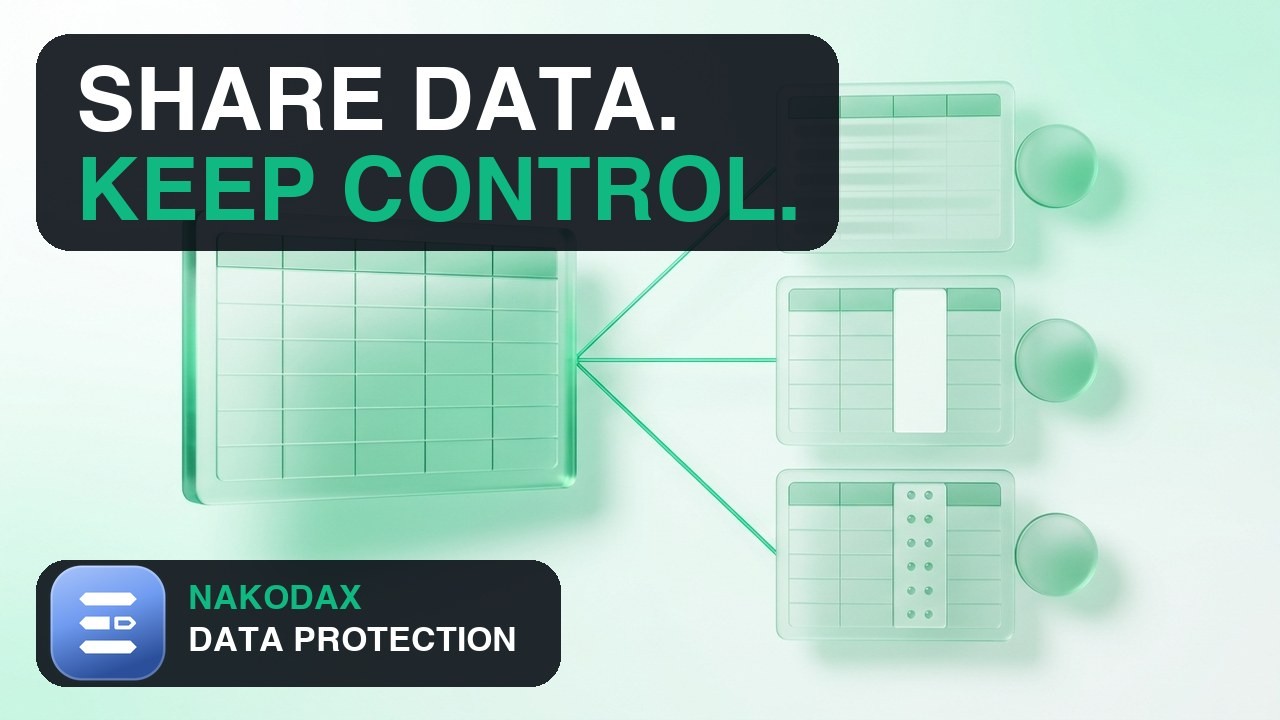
Data Protection: Share Data Without Losing Control
NakodaX Data Protection lets you send data to partners from the pipeline you already run: each partner gets only their own rows and columns, sensitive columns are hidden or scrambled, and you can end access anytime.
October 15, 2026
From the blog
Data Protection · 2 min read
Clean room or Data Protection: when do you use each?
A clean room is for joint analysis. Data Protection is for the files that still have to leave. Here is how each works, and why many teams use both.
September 10, 2026
Data Protection · 2 min read
How do you share a customer table with a vendor safely?
A vendor needs your customer data to do the work, but not all of it. Here is how to give each vendor their own file and end access when the contract ends.
August 24, 2026
Data Protection · 3 min read
How do you control old copies of customer data?
Old exports, backups and vendor copies are hard to find and delete. Protect the data before it leaves, and every copy made after is covered.
August 29, 2026
Seen in practice
Real situations, and the video where there is one, on the same problem.
Situation
Customer records held by an outsourcing vendor
Your outsourced team processed customer records for six years. Where are those files now? Truthfully: you don’t know.
Read moreSituation
Datasets that outlive the licence
You licensed your data for one use and one term. The term ends. The dataset doesn’t.
Read moreSituation
When sensitive data outlives the project it was shared for
A project needs your most sensitive records. A research partner, another organisation and an analytics contractor each get an extract. The project ends. The extracts don’t.
Read more